New Horizons
 Project Management Academy
 Six Sigma Online
 TCM Security
 TRACOM
 Velopi
 Watermark Learning
 Login

Get Started with NoSQL Injection (NoSQLi)
Overview NoSQL databases, a term that stands for “Not Only SQL,” represent a shift from traditional relational databases. Unlike their SQL-based counterparts that rely heavily on tables and fixed schemas, NoSQL databases provide flexible storage...
XPath Injection: A Beginners Guide
Overview XPath Injection, akin to other common injection attacks, specifically targets vulnerabilities within an application’s user input processing system. But what sets XPath Injection apart is its exploitation of XPath queries. The fallout? Unauthorized...
Start your Journey with Bug Bounty
Bug bounty programs have been a popular phenomenon in the tech industry for the last decade or so. They’re an opportunity for anyone to identify vulnerabilities in a company’s software or infrastructure and get rewarded for their discoveries. But, how do...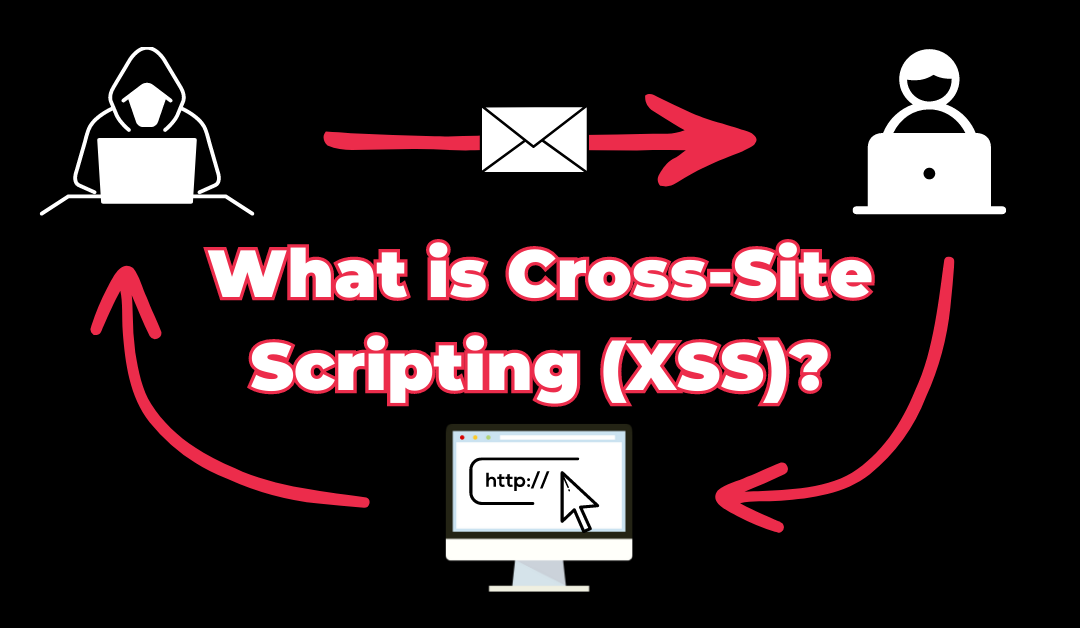
What is Cross-Site Scripting (XSS)?
Overview Cross-Site Scripting (XSS) is a type of security vulnerability in web applications that enables an attacker to insert malicious code into a web page that can be viewed by other users (typically in the form of scripts). When a web application fails to properly...